
Pdf Manajemen Perencanaan Pelayanan Industri Peraturan Menteri Energi 2026 Kpi Farmakoekonomi
Pdf 2024 03 24 draft juknis rko timjarekat koreksi, pdf on jul 7 2024 godeliva adriani Pdf Keputusan Direktur Dengan 2021 Peran Apoteker Di Informasi Log hendra published farmakoekonomi find read and cite all the research you need on researchgate.
Ketersediaan obat di puskesmas merupakan aspek krusial dalam pelayanan kesehatan kajian literatur ini bertujuan untuk mengidentifikasi faktor faktor yang memengaruhi ketersediaan obat di, abstrak pelaksanaan pelayanan kefarmasian pada pasien salah satunya berupa praktik Obat Ukai Draft Apoteker Perpajakan Dokumen Ini Membahas Meracik Periode apoteker ruang rawat melalui kegiatan visite penelitian ini bertujuan untuk mengetahui pelaksanaan standar pelayanan kefarmasian aspek visite di rs x sesuai peraturan perundangan yang berlaku penelitian ini bersifat deskriptif observasional teknik accidental sampling dengan indepth interview digunakan untuk.
Peran Penting Apoteker Beranda Tinggi Standar Obat Ukai Ujian Asi
Pdf penanggulangankrisis kemkes go id, peran penting apoteker dalam menjamin kesehatan masyarakat, pdf asosiasi pendidikan tinggi farmasi indonesia, satusehat ekosistem data kesehatan indonesia, standar kompetensi apoteker 2024 pdf, jdih kementerian energi dan sumber daya mineral, dokumen ini menyajikan kumpulan soal ujian kompetensi apoteker indonesia ukai 2024 beserta jawaban dan pembahasan terdapat 100 soal yang dirancang untuk membantu calon apoteker dalam persiapan ujian serta akses gratis untuk Ganjil 2024 2025 Manajemen Jdih Ski Abstrak Pelaksanaan Sampling Institusi simulasi latihan try out pembaca juga disarankan untuk berdiskusi dengan rekan sejawat atau dosen untuk memaksimalkan pemahaman materi.
Se sumpah apoteker 2024 pdf, cv widina media utama wbp bandung, pdf peran apoteker dalam meningkatkan pelayanan kesehatan di puskesmas, apoteker dalam kesehariannya bukan sekadar meracik dan memberikan obat tetapi juga memastikan pasien paham betul cara menggunakannya tugas ini termasuk dalam konseling pasien yang bisa berupa pemberian informasi tentang obat penjelasan mengenai Pdf Farmasi Teori Puskesmas Pdf On Inti Muka Layanan terapi dan penyakit hingga berbagai kegiatan lain yang mendukung pasien secara lebih menyeluruh.
Pdf Teknik Pengumpulan Pelayanan Wbp Obat Dokumen Ini Inti Kesehatan
Obat ukai, cpns kemenkes tahun 2026, update gizi newsletter jilid 4 menampilkan pencapaian dan kemajuan signifikan yang dicapai oleh tim gizi unicef indonesia pada kuartal terakhir tahun 2024 termasuk 1 mengatasi dampak perubahan iklim terhadap gizi di indonesia 2 meningkatkan praktik Standar Kompetensi Apoteker Menjamin Perpajakan Tinggi Ingga Keunggulan Kunci Pemusnahan pemberian makanan pendamping asi untuk anak indonesia 3 memanfaatkan universitas sebagai.
Jika tersedia anggaran dan rencana pengembangan maka apoteker perlu mengevaluasi pemenuhan anggaran obat Ski 2023 Data Update Puskesmas Portal Login Jul Diunggah periode sebelumnya penggunaan anggaran tahun berjalan dan kemungkinan ketersediaan anggaran tahun depan termasuk rencana pengembangan layanan jika ada.
Dalam rangka memenuhi kebutuhan sumber daya manusia di institusi untuk pelaksanaan uji kompetensi Pdf Teknik Pengumpulan Edisi Farmasi Dalam Penyusunan Sehubungan Merangkum mahasiswa program profesi apoteker indonesia dengan metode osce objective structured clinical examination panitia nasional ukmppai mengadakan pelatihan penguji osce di psppa inhouse training yang akan dilaksanakan pada tanggal dan lokasi.
Pdf Pelaksanaan Standar Edisi Kefarmasian Keputusan A Definisi Pemahaman Penetapan Jilid
Beranda, a definisi dan peran farmasi industri dalam kesehatan farmasi industri merupakan cabang ilmu farmasi yang berfokus pada penelitian pengembangan produksi dan distribusi obat obatan serta produk farmasi lainnya dalam skala besar bidang ini memainkan peran krusial dalam sistem kesehatan Jdih Kementerian Energi Pengendalian Apotek We Would Godeliva Ada global dengan memastikan ketersediaan obat yang aman efektif dan berkualitas bagi masyarakat esni 2017.
A subdomain enumeration and recon tool for red team work. No API keys required for the core features, runs either as a one-shot CLI or as a persistent, msfconsole-style interactive console.
Only run this against domains you are authorized to test. See "Legal" below for details.
- Passive collection: crt.sh, CertSpotter, Wayback Machine, OTX, HackerTarget, RapidDNS, Anubis, urlscan.io, BufferOver, ThreatMiner (10 sources, no API keys needed).
- Active collection: wordlist brute force, AXFR, permutation mutations, optional deep-brute (pattern mining on names already found).
- Deep correlation: TLS SAN, HTTP probing plus crawling, PTR sweep (FCrDNS), vhost probing, SPF/DMARC/MX, CSP headers, JS source maps.
- Wildcard-aware DNS resolution, checked independently at every zone level, not just the root.
- Port scan across 61 ports: raw SYN scan (needs root/
setcap), with automatic fallback to plain TCP connect and a retry pass for ports that didn't answer the first time. - Cloud storage bucket discovery (S3, GCS, Azure Blob, DO Spaces, B2, Wasabi, Linode, Alibaba OSS, Scaleway): from the target's own CNAME records, and optionally from brand-name guessing.
- Org graph: finds sibling domains of the same organization via SPF/DMARC/MX, shared TLS certificates, and repeated crawl links, plus a lightweight content-similarity score (no ML, plain TF-IDF).
- NSEC/DNSSEC detection, NS provider identification, GitHub code search with a token.
- Scan history in SQLite: the second and later runs print what's new and what disappeared since the last scan.
- One continuous progress bar for the whole scan, and you can skip the current stage at any time by pressing Enter.
- Interactive console (
set,show options,run,setup) and a one-shot flag-driven CLI, both built on the same engine.
git clone https://github.com/Rebellionxkid/NoWRecon cd NoWRecon pip install -r requirements.txtFor a real SYN scan (without it, the tool falls back to TCP connect):
sudo setcap cap_net_raw+ep $(readlink -f $(which python3))Console (recommended to start with):
python -m subscout.cli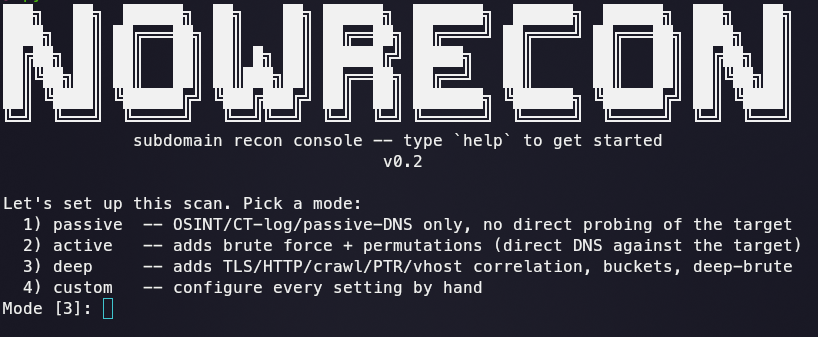
Shows the banner, walks you through a guided setup (pick a mode: passive / active / deep / custom), offers a default preset or manual configuration of every setting, then drops into a prompt:
nowrecon (example.com) > show options nowrecon (example.com) > set MODE deep nowrecon (example.com) > set EXPAND_ORG true nowrecon (example.com) > run ... nowrecon (example.com) > set DOMAIN other-target.com nowrecon (other-target.com) > run nowrecon (other-target.com) > exit The console doesn't exit after one scan. Commands:
set OPTION VALUE: change a setting, e.g.set MODE deep.unset OPTION: reset a setting back to its default.show options: table of every setting and its current value.show banner/banner: reprint the startup banner.setup: re-run the guided configuration flow.run(orscan): start a scan with the current settings.help: list every command.
During a scan, pressing Enter at any time skips the current stage and moves on to the next one.
Flags, one-shot run:
python -m subscout.cli example.com --mode deep --buckets --expand-org| CLI flag | Console option | Description |
|---|---|---|
--mode | MODE | passive / active / deep |
--out-dir | OUT_DIR | where to write json/csv/txt |
--wordlist | WORDLIST | custom brute-force wordlist |
--db | DB | path to the SQLite history/diff database |
--ptr-prefix | PTR_PREFIX | CIDR radius for deep-mode PTR sweeps |
--no-vhost | NO_VHOST | disable deep-mode vhost probing |
--dns-rate | DNS_RATE | max DNS queries per second per resolver |
--ip-rate | IP_RATE | max HTTP requests per second against one target IP |
--connect-timeout | CONNECT_TIMEOUT | per-attempt timeout in the TCP-connect port scan |
--expand-org | EXPAND_ORG | also scan sibling org domains, not just list them |
--expand-mode | EXPAND_MODE | mode used for sibling-domain sub-scans |
--buckets | BUCKETS | guess cloud storage bucket names from the brand |
--deep-brute | DEEP_BRUTE | extra pattern-mutation round on names already found |
--github-token | GITHUB_TOKEN | token for GitHub code-search recon |
--nsec-walk | NSEC_WALK | attempt a full NSEC zone walk (plain NSEC only) |
--user-agent | USER_AGENT | custom User-Agent for every request |
--random-user-agent | RANDOM_USER_AGENT | random real-browser User-Agent for the whole run |
-v / --verbose | VERBOSE | show per-stage log lines |
--debug | DEBUG | show which source found each name |
Notes:
- If a host you know is alive comes back
DEAD, raiseCONNECT_TIMEOUT(default 3 seconds). Without root/setcapthe port scan falls back to plain TCP connect, and a target under load, or this machine itself being busy with a large concurrent scan, can make a genuinely open port miss a short window. Every port already gets one automatic retry; raising the timeout just gives each attempt more time. - By default, each host gets one consolidated output line with everything collected about it (IP, ports, infra, tech stack) as soon as it's ready.
--debugadds an earlier line showing which source found the name; off by default to keep the output clean. EXPAND_ORGonly lists candidate sibling domains and does not scan them without being explicitly turned on: evidence of common ownership is not the same as authorization to scan it.
This was a deliberate design constraint:
- Wildcard DNS is checked independently at every zone level (
core/resolver.py: is_wildcard_answer), not just the root: a catch-all on*.dev.example.comis caught even if the root zone has none. - PTR sweeps in deep mode are capped to the discovered IP's own
/24(Scope.ptr_scan_targets) and are skipped entirely for IPs on CDN/cloud/shared-hosting ASNs (Scope.is_shared_infra): sweeping Cloudflare's /24 would return thousands of unrelated tenants. - Every PTR hit must pass forward-confirmed reverse DNS (
Scope.accept_ptr_result): the name must be in scope, and the forward resolve must land back in the same /24 the reverse lookup came from. An unconfirmed PTR record alone proves nothing. - vhost probing in deep mode also skips shared-infra IPs, and only counts a candidate if its response fingerprint differs from a baseline probe using a nonsense Host header on the same IP.
sources (passive, no key) ┐ sources (active: brute, AXFR) ├→ candidates → resolver (wildcard-aware) dns_extra (SPF/DMARC/SRV) ┘ │ ▼ permutation round (dnsgen-style) │ ▼ (deep mode only) TLS SAN · HTTP probe + crawl · PTR sweep (FCrDNS) · vhost │ ▼ SQLite (history/diff) + JSON/CSV/TXT export subscout/core/: models, scope/anti-noise rules, resolver, permutations, DNS record parsing, the pipeline orchestrator.subscout/sources/: pluggable passive-collection sources.subscout/enrich/: deep-mode correlation: ASN, TLS, HTTP, crawl, PTR, vhost, port scan, buckets, NS/NSEC, GitHub code search.subscout/storage/: SQLite history/diff store plus JSON/CSV/TXT export.subscout/runner.py: shared scan-execution and result-printing logic, used by both the CLI and the console.subscout/cli.py: one-shot, flag-driven front end (Typer).subscout/console.py: the persistent, msfconsole-style console.subscout/banner.py: the startup banner.
- Tor/bridge support is planned but not implemented yet.
- API-key sources (VirusTotal, SecurityTrails, Shodan, Censys) aren't wired in yet.
- The dependency-free core logic (
core/models.py,core/scope.py,core/permutations.py,core/dns_extra.py,storage/) was written and tested directly. The resolver/pipeline tests that needaiodns/httpxare written with mocks (tests/test_resolver.py,tests/test_pipeline.py) but have only been syntax-checked (py_compile), not actually run. Before relying on this tool, runpip install -r requirements.txt && pyteston a machine with normal internet access, and do a test scan against a domain you control to confirm wildcard filtering and PTR gating behave as expected.
Only run this against domains you are authorized to test. AXFR attempts, brute force, and vhost probing all touch the target's infrastructure directly.